


Pass RedHat Red Hat Certified Specialist in Ansible Automation Exam Exam in First Attempt Guaranteed Updated Dump from Pass4suresVCE!
Pass EX407 Exam with 42 Questions - Verified By Pass4suresVCE
RedHat EX407 Exam Syllabus Topics:
| Topic | Details |
|---|---|
| Topic 1 |
|
| Topic 2 |
|
| Topic 3 |
|
| Topic 4 |
|
| Topic 5 |
|
| Topic 6 |
|
| Topic 7 |
|
| Topic 8 |
|
| Topic 9 |
|
What is the duration of the EX407 Exam
- Format: Multiple choices, multiple answers
- Length of Examination: 4 hours
NEW QUESTION 15
Create an empty encrypted file called myvault.yml in /home/sandy/ansible and set the password to notsafepw. Rekey the password to iwejfj2221.
Answer:
Explanation:
ansible-vault create myvault.yml
Create new password: notsafepw Confirm password: notsafepw ansible-vault rekey myvault.yml
Current password: notsafepw New password: iwejfj2221 Confirm password: iwejfj2221
NEW QUESTION 16
Which of the following are shared between roles on the same system? (Choose all that apply.)
- A. Variables
- B. Tasks
- C. Handlers
- D. Templates
Answer: A,C
Explanation:
Variables are shared across roles on the same system. This is why namespacing is important. Handlers are shared across roles on the same system.
NEW QUESTION 17
Create a file called adhoc.sh in /home/sandy/ansible which will use adhoc commands to set up a new repository. The name of the repo will be 'EPEL' the description 'RHEL8' the baseurl is
'https://dl.fedoraproject.org/pub/epel/epel-release-latest-8.noarch.rmp' there is no gpgcheck, but you should enable the repo.
* You should be able to use an bash script using adhoc commands to enable repos. Depending on your lab setup, you may need to make this repo after you pass this task.
Answer:
Explanation:
See the Explanation for complete Solution below.
Explanation
chmod 0777 adhoc.sh
vim adhoc.sh
#I/bin/bash
ansible all -m yum_repository -a 'name=EPEL description=RHEL8
baseurl=https://dl.fedoraproject.org/pub/epel/epel-release-latest-8.noarch.rmp gpgcheck=no enabled=yes'
NEW QUESTION 18
Which is the default inventory file used by Ansible?
- A. ${PWD}/.inventory
- B. /etc/ansible/inventory
- C. /etc/hosts
- D. /etc/ansible/hosts
Answer: D
Explanation:
Ansbile refers to /etc/ansible/hosts as the default inventory.
NEW QUESTION 19
Create a playbook called timesvnc.yml in /home/sandy/ansible using rhel system role timesync. Set the time to use currently configured nip with the server 0.uk.pool.ntp.org. Enable burst. Do this on all hosts.
Answer:
Explanation:
Solution as: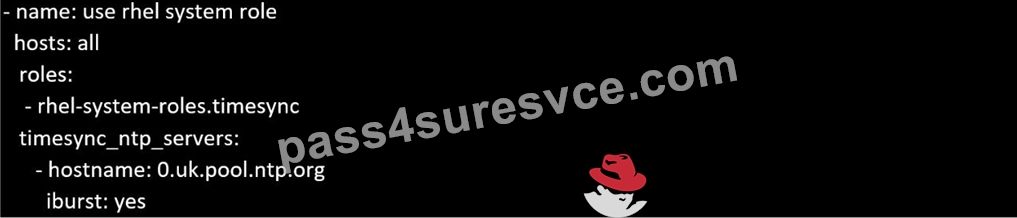
NEW QUESTION 20
What does the when keyword do?
- A. Allows a play to be conditional
- B. Allows a play to be scheduled
- C. Allows a task to be conditional
- D. There is no when keyword
Answer: C
NEW QUESTION 21
You are taking over for someone while they are away on leave. You need to run a playbook against over 600 servers. When you run the playbook you notice that only 10 servers are worked on at any one time.
How would you fix this so that you can have 50 servers worked on at the same time?
- A. Edit the /etc/ansible/hosts file and adjust the 'forks' parameter.
- B. Edit the /etc/ansible/ansible.cfg file and adjust the 'poll_interval' parameter.
- C. Edit the /etc/ansible/servers file and adjust the 'servers' parameter.
- D. Edit the /etc/ansible/ansible.cfg file and adjust the 'forks' parameter.
Answer: D
Explanation:
The forks parameter adjust the parallelism of the ansible commands.
NEW QUESTION 22
===================================================================================
control.realmX.example.com _ workstation.lab.example.com
node1.realmX.example.com _ servera.lab.example.com
node2.realmX.example.com _ serverb.lab.example.com
node3.realmX.example.com _ serverc.lab.example.com
node4.realmX.example.com _ serverd.lab.example.com
node5.realmX.example.com
- username:root, password:redhat
- username:admin, password:redhat
note1. don't change 'root' or 'admin' password.
note2. no need to create ssh-keygen for access, its pre-defined
note3. SELinux is in enforcing mode and firewalld is disabled/stop on whole managed hosts.
Use Ansible Galaxy with a requirements file called /home/admin/ansible/roles/
install.yml to download and install roles to /home/admin/ansible/roles from the
following URLs:
http:// classroom.example.com /role1.tar.gz The name of this role should be balancer
http:// classroom.example.com /role2.tar.gz The name of this role should be phphello
Answer:
Explanation:
Solution as:
# pwd
/home/admin/ansible/roles
# vim install.yml
---
- src: http://classroom.example.com/role1.tar.gz
name: balancer
- src: http://classroom.example.com/role2.tar.gz
name: phphello
:wq!
# pwd
/home/admin/ansible
# ansible-galaxy install -r roles/install.yml -p roles
NEW QUESTION 23
What is the primary difference between the shell and command module?
- A. The shell module is for executing shell commands, and the command module is for Ansible internal commands.
- B. The shell module sets a default shell whereas the command module executes a shell command.
- C. The shell module sets up a shell environment and the command module only runs the provided command.
- D. There is no difference.
Answer: C
NEW QUESTION 24
Consider the following playbook.
- hosts: webservers
become: yes
- name: install httpd
yum:
name: httpd
state: latest
Which line includes a syntax error?
- A. yum: - yum should be proceeded with a hyphen
- B. The file does not end with end-playbook.
- C. The playbook does not include the task directive.
- D. become: yes - there is no attribute called become
Answer: C
Explanation:
The "task:" directive is required at the prior to providing the tasks of a playbook. Without it, Ansible will not throw an error.
NEW QUESTION 25
Consider the following playbook:
# playbook name: /home/ansible/web.yml
---
- hosts: webservers
become: yes
tasks:
- name: edit file 1
lineinfile:
path: /var/www/content.hml line: "{{ text }}" tags:
- content
- name: edit file 2
lineinfile: path: /var/www/index.hml
line: "{{ text }}"
tags:
- web
- name: edit file 3
lineinfile:
path: /var/www/etc.hml
line: "{{ text }}"
tags: - content - misc
Which use of the ansible-playbook command on the provided playbook will result in ONLY editing the file /var/www/index.html?
- A. ansible-playbook /home/ansible/web.yml --skip-tags web
- B. ansible-playbook /home/ansible/web.yml --tags content
- C. ansible-playbook /home/ansible/web.yml
- D. ansible-playbook /home/ansible/web.yml --skip-tags content
Answer: D
Explanation:
This command skips the two tasks editing other files and only allows the task that is editing
/var/www/index.html to run.
NEW QUESTION 26
Create a jinja template in /home/sandy/ansible/ and name it hosts.j2. Edit this file so it looks like the one below. The order of the nodes doesn't matter. Then create a playbook in /home/sandy/ansible called hosts.yml and install the template on dev node at /root/myhosts
Answer:
Explanation:
Solution as:
NEW QUESTION 27
State whether the following statement is true or false.
The following command can be used to filter facts to pull out the ip address for the target host.
ansible local -m setup -a "filter=ansible_default_ipv4"
- A. False
- B. True
Answer: B
NEW QUESTION 28
Install and configure ansible
Userbobhas been created on your control node. Give him the appropriate permissions on thecontrol node.
Install the necessary packages to run ansible on the control node.
Create a configuration file /home/bob/ansible/ansible.cfg to meet the following requirements:
* The roles path should include /home/bob/ansible/roles, as well as any otherpath that may be required for the course of the sample exam.
* The inventory file path is /home/bob/ansible/inventory.
* Ansible should be able to manage 10 hosts at a single time.
* Ansible should connect to all managed nodes using the bobuser.
Create an inventory file for the following five nodes:
nodel.example.com
node2.example.com
node3.example.com
node4.example.com
node5.example.com
Configure these nodes to be in an inventory file where node1 is a member of groupdev.nodc2 is a member of group test, nodc3 is a member of group nodc4 and node 5 are members of groupprod.Also,prodis a member of group webservers.
Answer:
Explanation:
See the Explanation for complete Solution below.
Explanation
In/home/sandy/ansible/ansible.cfg
[defaults]
inventory=/home/sandy/ansible/inventory
roles_path=/home/sandy/ansible/roles
remote_user= sandy
host_key_checking=false
[privilegeescalation]
become=true
become_user=root
become_method=sudo
become_ask_pass=false
In /home/sandy/ansible/inventory
[dev]
node 1 .example.com
[test]
node2.example.com
[proxy]
node3 .example.com
[prod]
node4.example.com
node5 .example.com
[webservers:children]
prod
NEW QUESTION 29
What command is used to run a playbook?
- A. ansible <playbook>
- B. ansible-p <playbook>
- C. ansible-playbook <playbook>
- D. playbook <playbook>
Answer: C
Explanation:
This command will run a given playbook successfully.
NEW QUESTION 30
Create a file called requirements.yml in /home/sandy/ansible/roles a file called role.yml in
/home/sandy/ansible/. The haproxy-role should be used on the proxy host. And when you curl
http://node3.example.com it should display "Welcome to node4.example.com" and when you curl again
"Welcome to node5.example.com" The php-role should be used on the prod host.
Answer:
Explanation:
See the Explanation for complete Solution below.
Explanation
Solution as:
Check the proxy host by curl http://node3.example.com
NEW QUESTION 31
State whether the following statement is true or false.
Will this command use servers in a local inventory called invent.local?
ansible all -m ping -i invent.local
- A. False
- B. True
Answer: B
NEW QUESTION 32
===================================================================================
control.realmX.example.com _ workstation.lab.example.com
node1.realmX.example.com _ servera.lab.example.com
node2.realmX.example.com _ serverb.lab.example.com
node3.realmX.example.com _ serverc.lab.example.com
node4.realmX.example.com _ serverd.lab.example.com
node5.realmX.example.com
- username:root, password:redhat
- username:admin, password:redhat
note1. don't change 'root' or 'admin' password.
note2. no need to create ssh-keygen for access, its pre-defined
note3. SELinux is in enforcing mode and firewalld is disabled/stop on whole managed hosts.
Create a playbook called web.yml as follows:
* The playbook runs on managed nodes in the "dev" host group
* Create the directory /webdev with the following requirements:
--> membership in the apache group
--> regular permissions: owner=r+w+execute, group=r+w+execute, other=r+execute
s.p=set group-id
* Symbolically link /var/www/html/webdev to /webdev
* Create the file /webdev/index.html with a single line of text that reads:
"Development"
--> it should be available on http://servera.lab.example.com/webdev/index.html
Answer:
Explanation:
Solution as:
# pwd
/home/admin/ansible/
# vim web.yml
---
- name:
hosts: dev
tasks:
- name: create group
yum:
name: httpd
state: latest
- name: create group
group:
name: apache
state: present
- name: creating directiory
file:
path: /webdev
state: directory
mode: '2775'
group: apache
- sefcontext:
target: '/webdev/index.html'
setype: httpd_sys_content_t
state: present
- name: Apply new SELinux file context to filesystem
command: restorecon -irv
- name: creating symbolic link
file:
src: /webdev
dest: /var/www/html/webdev
state: link
force: yes
- name: creating file
file:
path: /webdev/index.html
sate: touch
- name: Adding content to index.html file
copy:
dest: /webdev/index.html
content: "Development"
- name: add service to the firewall
firewalld:
service: http
permanent: yes
state: enabled
immediate: yes
- name: active http service
service:
name: httpd
state: restarted
enabled: yes
:wq
# ansible-playbook web.yml --syntax-check
# ansible-playbook web.yml
NEW QUESTION 33
......
How to study the EX407 Exam
There are two main types of resources for preparation of certification exams first there are the study guides and the books that are detailed and suitable for building knowledge from ground up then there are video tutorial and lectures that can somehow ease the pain of through study and are comparatively less boring for some candidates yet these demand time and concentration from the learner. Smart Candidates who want to build a solid foundation in all exam topics and related technologies usually combine video lectures with study guides to reap the benefits of both but there is one crucial preparation tool as often overlooked by most candidates the practice exams. Practice exams are built to make students comfortable with the real exam environment. Statistics have shown that most students fail not due to that preparation but due to exam anxiety the fear of the unknown. Pass4suresVCE expert team recommends you to prepare some notes on these topics along with it don't forget to practice Red Hat EX407 exam dumps which have been written by our expert team, Both these will help you a lot to clear this exam with good marks.
Penetration testers simulate EX407 exam: https://www.pass4suresvce.com/EX407-pass4sure-vce-dumps.html
Free Test Engine For Red Hat Certified Specialist in Ansible Automation Exam Certification Exams: https://drive.google.com/open?id=1KD0yqnIa15XExrgkGRbh173zn9cdBtLD